

Hello! Yes, it's all a disaster again! Let's get this party started: No comments today, so imagine this:We wrote something that we find very funny,Nobody else gets it,But everyone humors us Just like a typical watchTowr Labs blog introduction.As with all watchTowr
一、核心思路
- 【方法模板·非来源原文】【多步骤流程的信任模型错位(每步各自校验、步骤间主体不一致)】画状态机:每步 输入 / 服务端产出 / 会话或 token / 下一步依赖,缺一步会误判
- 来源链接: https://labs.watchtowr.com/the-internet-is-falling-down-falling-down-falling-down-cpanel-whm-authentication-bypass-cve-2026-41940/
- 分类命中词: {'Authentication Bypass': ['authentication bypass'], 'Path Traversal / LFI': ['directory traversal'], 'Command Injection / RCE': ['rce'], 'Cloud Security / IAM / Storage': ['oss']}
落到 QGG 怎么用
可直接落到 QGG 的「Authentication Bypass」测试清单:【多步骤流程的信任模型错位(每步各自校验、步骤间主体不一致)】画状态机:每步 输入 / 服务端产出 / 会话或 token / 下一步依赖,缺一步会误判;仅可生成人工核查清单(缺请求级证据,禁自动生成生产模板)
二、成立条件
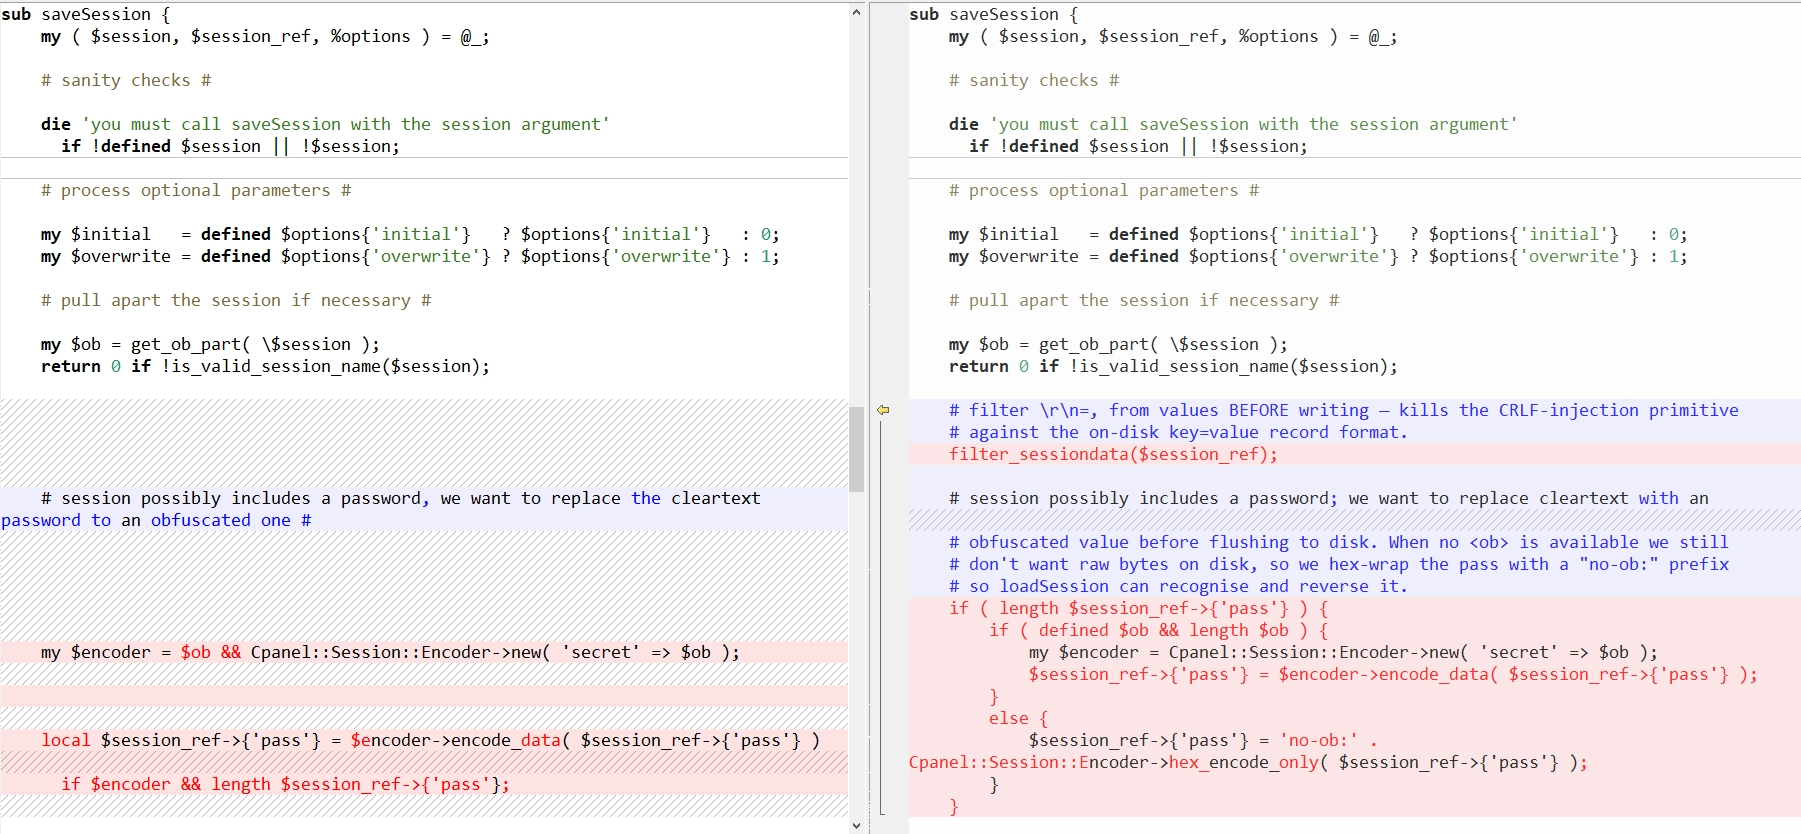
- 【来源原文片段】, in case you're asking - "but doesn't the encoder still encode pass to hex?" - only if $ob is non-empty. And $ob comes from the cookie:my $session = $server_obj->get_c
三、验证方法与步骤
- 【方法模板·非来源原文】【多步骤流程的信任模型错位(每步各自校验、步骤间主体不一致)】画状态机:每步 输入 / 服务端产出 / 会话或 token / 下一步依赖,缺一步会误判
- 【方法模板·非来源原文】【多步骤流程的信任模型错位(每步各自校验、步骤间主体不一致)】身份来源标注:每步服务端认定的身份来自输入参数、会话 cookie、数据库、还是上一步响应?
- 【方法模板·非来源原文】【多步骤流程的信任模型错位(每步各自校验、步骤间主体不一致)】步骤跳跃与乱序:直达 step3/step4、跳过 step2、重放 step1 的响应推进 step2
- 【方法模板·非来源原文】【多步骤流程的信任模型错位(每步各自校验、步骤间主体不一致)】参数替换:在某一步替换主体标识(手机号/邮箱/uid),观察最终写入落在谁身上
- 【方法模板·非来源原文】【多步骤流程的信任模型错位(每步各自校验、步骤间主体不一致)】响应篡改:改 success/code/step/returnkey,看服务端是否采信客户端结论
- 【方法模板·非来源原文】【多步骤流程的信任模型错位(每步各自校验、步骤间主体不一致)】state token 跨主体:把 returnkey/flow_id 换到另一会话,是否跨主体生效(只读判定)
- 【方法模板·非来源原文】【多步骤流程的信任模型错位(每步各自校验、步骤间主体不一致)】终态核对:改密/改绑后用'原身份'与'目标身份'分别登录,确认到底改了谁
- 【方法模板·非来源原文】入口发现:登录/重置/SSO 回调/验证码/记住我/多因子各分支
- 【方法模板·非来源原文】测试变量:字段省略(如 captcha 整体不传)、类型污染、大小写、注释截断、响应篡改
- 【方法模板·非来源原文】成功证据:无凭据拿到受保护资源(带响应体)或进入他人账号
- 【方法模板·非来源原文】误报过滤:仅 302 到首页不算;必须验证会话真的可访问受保护页面
【缺失】来源未给出可执行复现步骤;需按 test_methodology 在授权靶场自行设计并记录
四、误报排除
- 登录页/统一错误页/WAF 阻断页/缓存页/通用 200 空壳
- 非确定性字段(traceId/timestamp/随机 token)必须先归一化
反向证据
- 【未记录】来源未讨论误报或反向结果
五、影响与修复
影响:
分类:Authentication Bypass;来源严重性:未提供。实际影响需以本地/授权靶场复现结果为准,评分与来源自述不构成影响结论。
修复:
统一鉴权中间件覆盖全部路由,验证码字段缺失即拒绝,禁止客户端可控的信任标记。
关联:CVE-2026-41940
Comments | NOTHING