

Part 1 of this week's saga can be found here.This research is a glimpse into the capabilities that power our Preemptive Exposure Management solution, enabling organizations to rapidly react to emerging threats: the watchTowr Platform.What Is A Citrix NetScaler?NetScaler, from Citrix (now under Cloud
一、核心思路
- 【方法模板·非来源原文】入口发现:从 JS/路由/流量/历史路径交叉确认该漏洞类别的输入面,单一样本不下结论
- 来源链接: https://labs.watchtowr.com/here-we-go-again-citrix-netscaler-dtls-preauth-memory-overflow-cve-2026-88772/
- 分类命中词: {'Command Injection / RCE': ['rce', 'remote code execution'], 'HTTP Request Smuggling': ['request smuggling']}
可直接落到 QGG 的「Command Injection / RCE」测试清单:入口发现:从 JS/路由/流量/历史路径交叉确认该漏洞类别的输入面,单一样本不下结论;可生成部分自动化规则候选(有请求级证据)
二、成立条件
- 【来源原文片段】space.At [4], reject the message if that NSB will not fit.At [5], copy the NSB only after the check passes.At [6], subtract the number of copied bytes, then repeat the ch
三、验证方法与步骤
- 【方法模板·非来源原文】入口发现:从 JS/路由/流量/历史路径交叉确认该漏洞类别的输入面,单一样本不下结论
- 【方法模板·非来源原文】前置条件:记录认证状态、角色、数据所有权、组件与版本
- 【方法模板·非来源原文】测试变量:参数位置、对象标识、方法、请求头、数据格式、状态切换
- 【方法模板·非来源原文】成功证据:真实数据读取/命令执行回显/状态真实变更(可复现,带原始报文)
- 【方法模板·非来源原文】误报过滤:登录跳转、统一错误页、WAF 阻断页、缓存内容、通用 200、非确定性字段
- 【方法模板·非来源原文】影响确认:只读证明优先;写操作仅在自建 canary 对象上做一次最小验证
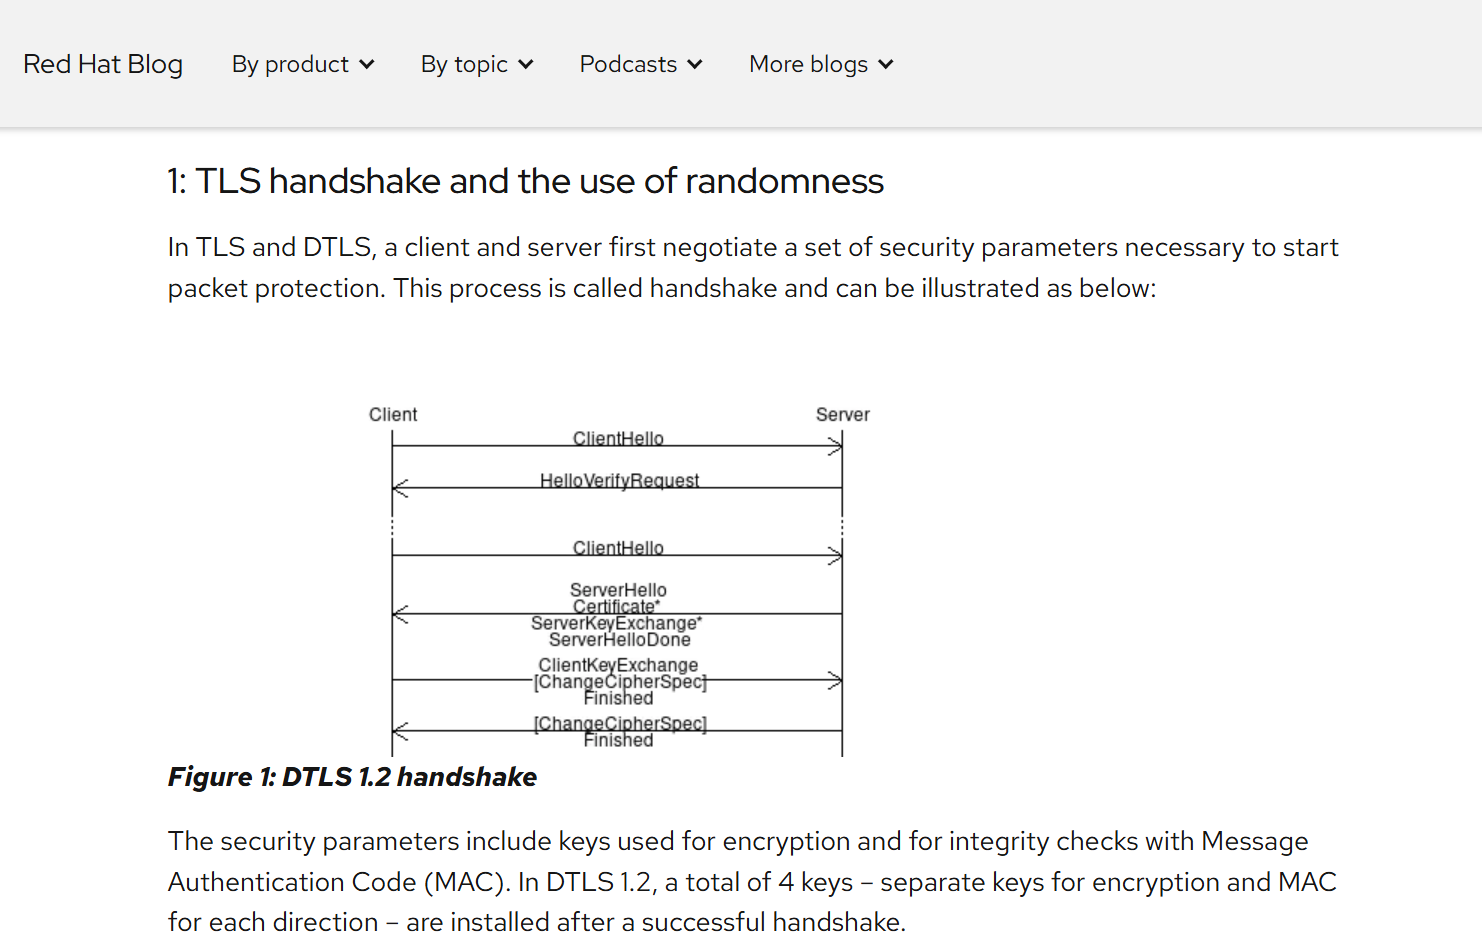
Step 1: Pass the DTLS Cookie CheckThe server does not accept a large first packet from a new DTLS client. It first asks the client to return a cookie. This only proves that the client can receive packets at its IP address; it does not authenticate a user.Source: Red Hat, "Understanding the DTLS all-
四、误报排除
- 登录页/统一错误页/WAF 阻断页/缓存页/通用 200 空壳
- 非确定性字段(traceId/timestamp/随机 token)必须先归一化
- 【未记录】来源未讨论误报或反向结果
五、影响与修复
影响:
分类:Command Injection / RCE;来源严重性:未提供。实际影响需以本地/授权靶场复现结果为准,评分与来源自述不构成影响结论。
修复:
按该类漏洞的通用根因修复(服务端校验/白名单/最小权限),并补充回归测试。
关联:CVE-2026-88771、CVE-2026-88772、CVE-2026-88773、CVE-2026-88774、CVE-2026-88775、CVE-2026-88776、CVE-2026-88777、CVE-2026-88778
Comments | NOTHING